2025 Gvenilir Casino Siteleri – En yi Kazandran Slot Siteleri.4949

2025 Güvenilir Casino Siteleri – En İyi Kazandıran Slot Siteleri

▶️ OYNAMAK

Содержимое

En iyi casino siteleri arıyorsanız, canlı casino siteleri ve casino bahis siteleri arasında seçim yapmanız gerekmektedir. Güvenilir casino siteleri sizin için en iyi deneyim sunmalıdır. Bu yıl, deneme bonusu veren casino siteleri de sizin için ideal seçenekler arasında yer alabilir.

Canlı casino siteleri ile oynarken, profesyonel cüzzamlılarla canlı oyun oynayabilirsiniz. Casino bahis siteleri ise çeşitli oyun türleri sunarak, her tür oyun sevgiliniz için en iyi deneyim sunarlar.

Deneme bonusu veren casino siteleri ile başlayabilirsiniz. Bu siteler, yeni kullanıcılar için ücretsiz oyun deneme fırsatı sunarlar. Bu, sizin oyunlarınızda kazanma olasılıklarını anlamak için ideal bir yol olabilir.

2025 yılı için en iyi casino siteleri arasından seçim yaparken, güvenilirlik, çeşitli oyun seçenekleri ve deneme bonusları gibi faktörleri göz önünde bulundurmanız önemlidir.

En İyi Slot Casino Siteleri

2025 yılında güvenilir slot casino siteleri arasında en iyi olanları seçmek zor olabilir. Ancak, Canlı Casino Siteleri ve en güvenilir casino siteleri arasında seçim yapmak kolaylaşır. İşte önerilerimiz:

Slot Casino Siteli
Özellikler
Slot Casino A Yüksek kazanma oranları, çeşitli bonuslar ve güvenli ödeme sistemleri. Slot Casino B Yeni slot oyunları, canlı dealer oyunları ve profesyonel müşteri hizmetleri. Slot Casino C En iyi grafikler ve kullanıcı dostu arayüz, güvenilir ödeme sistemleri.

Her slot casino sitesi kendi unvanını kazandırmak için çeşitli yollarla çaba gösterir. En iyi casino siteleri arasında yer almak için güvenilirlik, güvenli ödeme sistemleri ve çeşitli bonuslar gereklidir. Ayrıca, canlı dealer oyunları ve yeni slot oyunları da bu sitelerin popülerliğini artırır.

Yeni casino siteleri de bu özelliklere sahip olabilir. En güvenilir casino siteleri arasında yer almak için, sitenin yetkili kurumların onayını alıp almadığını kontrol etmek önemlidir. Ayrıca, sitenin kullanıcılarına güvenli bir ödeme sistem sunup sunmadığını ve çeşitli bonuslar sunup sunmadığını öğrenmek de faydalıdır.

En İyi Güvenilir Kasino Sitelerinin Seçimi

  • Deneme bonusu veren casino siteleri seçin. Bu, yeni kullanıcıların platforma alışma sürecini kolaylaştırır ve deneyimini iyileştirir.
  • Slot casino siteleri arayışında, geniş ve çeşitlilik sunan siteleri tercih edin. Bu, kazanma şansınızı artırır ve oyun çeşitliliğini artırır.
  • Canlı casino siteleri için profesyonel bir deneyim arıyorsanız, canlı dealer oyunları ve canlı destek hizmetleri sunan siteleri seçin. Bu, oyun deneyiminizi gerçekçi hale getirir.
  • En iyi casino siteleri arasında güvenilirlik ve güvenliği ön planda tutan siteleri arayın. Bu, bilgilerinizi ve paralarınızı korur.
  • Yeni casino siteleri için, kullanıcı yorumlarını ve deneyimlerini inceleyin. Bu, güvenilir ve güvenli bir platforma yatırım yapmanızı sağlar.
  • En İyi Slot Oyunları

    Canlı casino siteleri arasında en kazançlı slot oyunlarını bulabilirsiniz. En güvenilir casino siteleri, deneme bonusu veren ve en güvenilir casino siteleri arasında seçebileceğiniz siteler arasında bulunan slot oyunları en iyi seçeneğinizdir. Bu siteler, çeşitli oyun türlerini sunar ve her kullanıcıya özel bir deneyim sunar. Öncelikle, güvenilir bir casino sitesini seçmek için deneme bonusu veren siteleri araştırmanızı öneririm. Bu, oyunları deneyebilmeniz ve en uygun oyunu bulmanıza yardımcı olur. En güvenilir casino siteleri arasında bulunan canlı casino siteleri, profesyonel bir atmosfer sunar ve canlı cüzzamlı dealerlerle oynanabilir slot oyunları ile ilgili daha fazla bilgi edinebilirsiniz. Bu siteler, çeşitli slot oyunları ve bonuslar sunarak, her kullanıcı için en iyi deneyim sunar. Deneme bonusu veren casino siteleri, yeni kullanıcılar için ücretsiz oyun deneme fırsatı sunar. Bu, oyunları deneyebilmeniz ve kazanma stratejilerinizi geliştirmenizi sağlar. En güvenilir casino siteleri arasında bulunan canlı casino siteleri, en iyi slot oyunlarını sunar ve her kullanıcıya özel bir deneyim sunar. Bu siteler, güvenilirlik, deneme bonusları ve canlı dealerlerle birlikte, en iyi slot oyunlarını sunar.

    Güvenliğinizle İlgili Sorunların Çözümü

    Yeni casino siteleri seçtiğinizde güvenliğinize dikkat etmeniz gerekmektedir. En iyi casino siteleri arasında güvenilir ve güvenli seçenekler bulunmaktadır. Live casino siteleri ve slot casino siteleri arasında seçim yaparken, güvenliğinizle ilgili sorunları çözmek için deneme bonusu veren siteleri de göz önünde bulundurmanız önemlidir. Bu siteler, deneme bonusu ile yeni kullanıcılar için güvenli bir ortam sağlar ve riski azaltır. Güvenliğinizle ilgili herhangi bir sorun yaşarsanız, sitenin müşteri hizmetleriyle iletişime geçmeniz gerekmektedir. Müşteri hizmetleri, sorunlarınızı hızlı ve etkin bir şekilde çözmenize yardımcı olur. Eğer sitenin müşteri hizmetleriyle iletişim kuramıyorsanız, güvenliğinizle ilgili sorunları başka güvenilir sitelerdeki müşteri hizmetleriyle paylaşabilirsiniz. Bu, güvenliğinizle ilgili herhangi bir sorununuzun çözüldüğü bir ortam sağlar.

    2025 Gvenilir Casino Siteleri – En yi Kazandran Slot Siteleri.1625

    2025 Güvenilir Casino Siteleri – En İyi Kazandıran Slot Siteleri

    ▶️ OYNAMAK

    Содержимое

    Rekomendasyonumuz: Deneme bonusu veren casino siteleri – bu siteler, yeni oyuncular için güvenli bir giriş imkanı sunar. Deneme bonusu ile yeni slot oyunları deneyebilir ve stratejilerini geliştirebilirsiniz.

    Casino bahis siteleri arasında en güvenilir olanları seçmek zor olabilir. Ancak, canlı casino siteleri, canlı cihazlarla oynanması halinde oyunların gerçek bir deneyimi sunar. Bu siteler, oyuncuların gerçek bir sosyal deneyimi yaşamasına olanak tanır.

    En iyi casino siteleri genellikle güvenilirlik, güvenlik ve sundukları oyun çeşitliliği açısından değerlendirilir. Bu siteler, kullanıcıların ihtiyaçlarına ve tercihlerine göre çeşitli oyunlar sunar. Ayrıca, profesyonel bir müşteri hizmeti ekibi ile iletişim kurabilirsiniz.

    Önerimiz, deneme bonusu veren ve canlı casino siteleri olan en güvenilir casino siteleri arasından seçim yapmaktır. Bu siteler, oyuncuların deneyimi ve kazanma şanslarını artıracak şekilde tasarlanmıştır.

    En İyi Slot Casino Siteleri

    2025 için güvenilir casino siteleri arasında slot casino siteleri en popüler kategori olacak. Önerimizden yola çıkarak, en iyi slot casino sitelerini bulabilirsiniz. Öncelikle, güvenilir casino siteleri arasında yer alan Yeni Casino Siteleri listesini inceleyin. Bu siteler, kullanıcı dostu arayüzler, çeşitli slot oyunları ve deneme bonusu ile öne çıkmaktadır.

    Diğer önerilerimiz arasında Canlı Casino Siteleri de yer alıyor. Bu sitelerde canlı cihazlarla oynanabilecek slot oyunları ile eğlence deneyiminizi artırabilirsiniz. Ayrıca, en iyi casino siteleri arasında Deneme Bonusu Veren Casino Siteleri de yer alıyor. Bu siteler, yeni kullanıcıların deneme oyunları ile tanışmasını sağlar ve oyunları daha iyi anlamalarına yardımcı olur.

    Seçtiğiniz slot casino siteleri güvenilir olmalı. Bu nedenle, sitelerin lisanslı olduğunu ve güvenli ödeme sistemlerini kullanıp kullanmadığını kontrol edin. Ayrıca, sitelerin kullanıcı yorumlarını ve müşteri hizmetlerini inceleyin. Bu bilgiler, güvenilir bir slot casino sitesini seçmenize yardımcı olacaktır.

    En İyi Güvenilir Kasino Sitelerinin Seçimi

    En güvenilir slot casino siteleri arasında deneme bonusu veren casino siteleri yer alıyor. Bu siteler, yeni kullanıcıları teşvik etmek için özel teklifler sunar. Öncelikle, güvenilir casino siteleri genellikle uluslararası lisanslar ve güvenlik standartlarını sağlar. Bu, sitenin güvenilir olduğunu ve verilerin korunacağını gösterir. Ayrıca, kullanıcıların para yatırma ve çekme işlemlerini kolaylaştıran çeşitli ödeme yöntemleri sunan siteler de en iyi seçenekler arasındadır.

    En iyi güvenilir casino siteleri arasında slot casino siteleri de yer alıyor. Bu siteler, çeşitli oyun türleri ve temiz, kullanıcı dostu arayüzler sunarak oyun deneyimini iyileştirir. Ayrıca, yeni casino siteleri de bu listeye dahil olabilir, çünkü bu siteler genellikle en güncel ve popüler oyunları sunar. Güvenilir casino siteleri, kullanıcıların güvenli bir şekilde oynayabilecekleri bir ortam sağlar ve bu, oyun deneyiminin kalitesini artırır.

    • Deneme bonusu veren casino siteleri, kullanıcıların oyunları deneyimlemek için güvenli bir ortam sağlar.
    • Slot casino siteleri, çeşitli oyun türleri ve kullanıcı dostu arayüzler sunarak oyun deneyimini iyileştirir.
    • Yeni casino siteleri, en güncel ve popüler oyunları sunarak kullanıcıların oyun deneyimini artırır.

    En İyi Slot Oyunları

    Deneme bonusu veren casino siteleri ile başlayalım. Bu siteler, yeni kullanıcıları teşvik etmek için çeşitli deneme bonusları sunar. Örneğin, Canlı Casino Siteleri genellikle en iyi slot oyunlarını deneme bonusu ile sunar. Bu, sizin için ücretsiz deneme fırsatı sunar ve oyunları daha iyi öğrenmenize yardımcı olur.

    Güvenilir Casino Siteleri genellikle en iyi slot oyunlarını sunar. En Güvenilir Casino Siteleri arasında Yeni Casino Siteleri de yer alır. Bu siteler, güvenilirlik ve güvenliği önceliğe alan büyük casino grupları tarafından işletilir. Bu nedenle, bu sitelerde oynayarak kazanma şansınızı artırabilirsiniz.

    Casino Bahis Siteleri arasında da en iyi slot oyunları bulunur. Bu siteler, çeşitli oyun türlerini sunar ve her kullanıcı için en uygun oyunları bulmanıza yardımcı olur. En Güvenilir Casino Siteleri arasında Canlı Casino Siteleri de yer alır. Bu sitelerde canlı croupier ile oynanabilecek slot oyunları bulunur. Bu, oyun deneyiminizi daha fazla zenginleştirir.

    Güvenliğinizle İlgili Sorunların Çözümü

    En iyi slot casino siteleri için güvenliğinizle ilgili herhangi bir sorununuz olursa, canlı casino siteleri ile iletişime geçin. Yeni casino siteleri ve en güvenilir casino siteleri arasında seçim yaparken, güvenliği önceliğe koymalısınız. Eğer bir sorun yaşarsanız, canlı destek ekibinden hemen yardım isteyin. Bu ekibin size hızlı ve etkin bir şekilde yardımcı olacağını unutmayın.

    En güvenilir casino siteleri genellikle kullanıcıların güvenliğini önemsiyor ve sorunları çözmek için çeşitli yöntemler kullanıyor. Eğer bir sitenin güvenliği hakkında endişeleniyorsanız, onun güvenlik politikalarını ve belgelerini inceleyin. Bu, sitenin güvenliğini sağlama çabalarını anlamak için iyi bir yol.

    En güvenilir casino siteleri genellikle kullanıcıların bilgilerini şifreliyor ve güvenli bağlantılar kullanıyor. Bu, sizin bilgilerinizi korumak için önemli bir adımdır. Eğer bir sitenin bu özelliklerini sunmıyorsa, güvenliğinizle ilgili sorunlar yaşayabilirsiniz. Bu nedenle, güvenliğinizle ilgili herhangi bir sorun yaşarsanız, canlı casino siteleri ile iletişime geçin ve sorununuzun çözümlenmesini sağlayın.

    DeFi dApp Integration Is Not a Connection Problem—It Is a Risk-Interpretation Problem

    A common misconception in decentralized finance is that a wallet is safe once it connects to the right website. In practice, the connection is only the beginning. A decentralized application, or dApp, can request a signature, create token approvals, route a swap through several contracts, or submit a transaction whose final economic effect is difficult to see from a short prompt. The important question is not simply, “Can this wallet connect?” It is, “Can the user understand what the connection and transaction will permit?”

    That distinction matters because DeFi risk sits at the boundary between software and judgment. Smart contracts may execute exactly as written, yet the user may misunderstand what was authorized. A wallet can improve visibility, simulation, and warning signals, but it cannot make an unaudited protocol trustworthy or eliminate every unfamiliar risk. For US-based users managing assets across Ethereum and other EVM-compatible networks, the practical comparison is therefore between different layers of control: basic browser-wallet integration, advanced transaction-aware wallets, and more deliberate operational setups that combine wallet safeguards with independent verification.
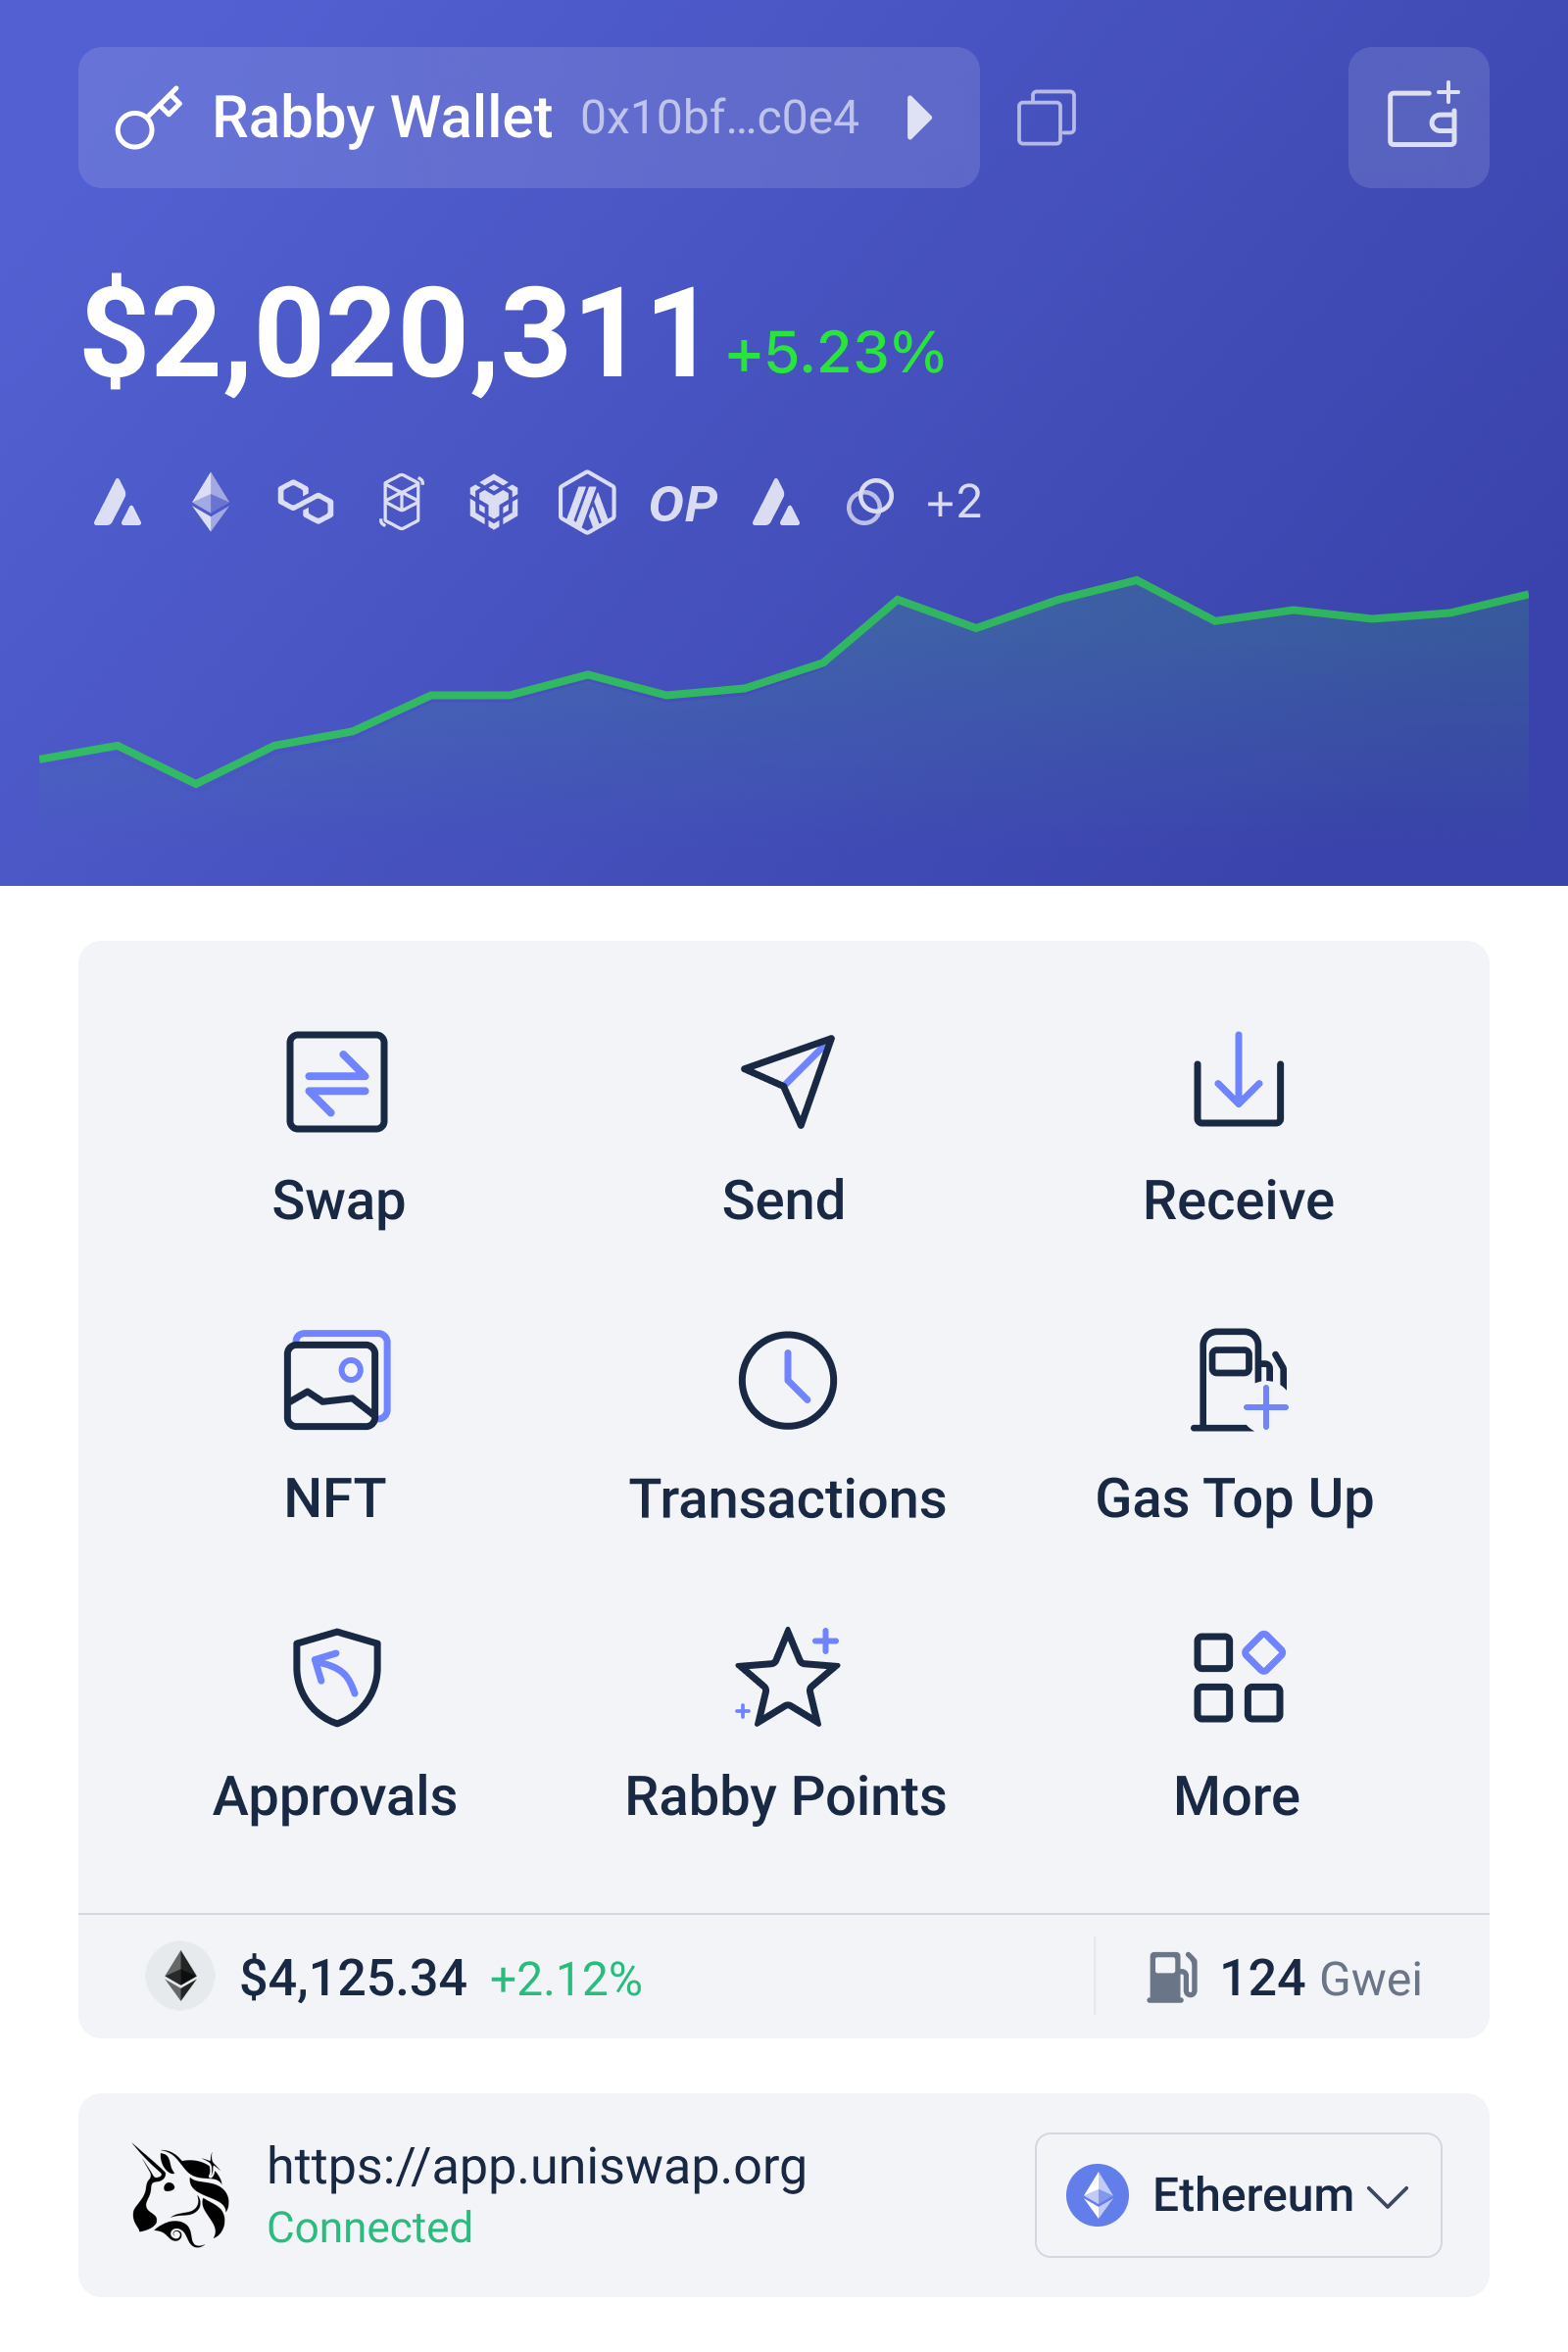
    Wallet interface illustrating how transaction details and DeFi contract interactions can be evaluated before signing

    Three approaches to connecting with DeFi protocols

    The simplest approach is a conventional browser wallet that exposes a dApp’s connection request and asks the user to approve signatures. This is convenient and often sufficient for familiar applications, especially when the user understands the network, contract, and asset involved. Its weakness is that convenience can compress a complicated transaction into a generic “confirm” action. The wallet may show a contract address and estimated gas, but those fields do not necessarily explain whether a user is granting spending authority, trading one asset for another, or interacting with a contract that has unexpected logic.

    A second approach is a transaction-aware wallet that adds simulation and contextual risk signals before signing. Simulation attempts to model the likely state changes: which tokens leave the wallet, which assets arrive, whether an approval is created, and whether the transaction is likely to fail. This changes the user’s task from reading raw calldata—a technical encoding of contract instructions—to reviewing an estimated outcome. Tools such as here can be useful in this layer because the wallet becomes an interpretation interface rather than merely a key-management tool.

    The third approach is a high-discipline setup: a separate signing device or hardware wallet for material balances, a smaller active wallet for experimentation, explicit approval management, and manual checks of domains and contract addresses. This offers stronger compartmentalization, but it also introduces friction. A hardware wallet can protect private keys from many malware scenarios while still allowing a user to approve a malicious transaction. Security improves only if the transaction details are understandable on the signing path and the user is willing to stop when the information is unclear.

    These approaches are not mutually exclusive. A user might use a transaction-aware browser wallet for routine DeFi activity, a hardware signer for long-term holdings, and a dedicated test wallet for new protocols. The best design depends on exposure. A small liquidity experiment and a six-figure treasury should not share the same assumptions, even if both use the same blockchain and dApp interface.

    Why simulation helps—and where it can mislead

    Transaction simulation is valuable because it addresses a fundamental asymmetry in DeFi: contracts are deterministic at execution, but the user interface may be ambiguous before execution. If a proposed transaction predicts that a wallet will lose a large amount of a token while receiving nothing meaningful, that is a powerful reason to stop. Likewise, a warning about an unlimited approval can reveal a risk that is easy to miss when a user is focused on a swap or yield opportunity.

    Yet simulation is not a guarantee. It is a forecast under particular assumptions about blockchain state, pricing, block timing, and contract behavior. A transaction may be simulated against one state and executed against another. Market prices can move, liquidity can change, and a contract can depend on information that evolves between signing and inclusion. Some protocols also use upgradeable contracts, external price feeds, callbacks, or complex routing logic that makes the economic outcome harder to summarize completely.

    The boundary condition is especially important for approvals. An approval is not the same as a transfer, but it can give a contract permission to transfer tokens later, subject to the allowance. Revoking unused approvals reduces one attack surface, yet it does not repair a compromised protocol, reverse a completed transaction, or protect a user who signs a new malicious approval. Approval hygiene is risk reduction, not risk elimination.

    There is a related distinction between wallet-level and protocol-level security. A wallet can identify suspicious patterns, flag a risky contract, and make the expected result clearer. It cannot prove that a lending market’s collateral model will remain solvent, that an oracle will remain accurate, or that a bridge’s validators will behave honestly. The wallet helps with authorization risk; it does not fully underwrite economic, governance, liquidity, or smart-contract risk.

    A practical framework for assessing a new dApp

    Before connecting, verify the domain through a trusted route rather than a search advertisement or unsolicited message. Check the intended network and confirm that the dApp’s purpose matches the action being requested. A site that claims to offer a token claim but requests permission to move unrelated assets deserves immediate suspicion.

    Before signing, classify the request. Is it a read-only connection, a message signature, an approval, a swap, a deposit, a withdrawal, or an administrative action? These categories carry different consequences. A message signature may not move funds immediately, but it can still be dangerous when used in phishing systems or off-chain authorization schemes. A token approval may appear routine while creating a future pathway for asset movement.

    Then compare the intended economic result with the simulated result. Look for the assets leaving the wallet, the assets arriving, the spender address, the approval amount, and any unexpected contract calls. If the result is unavailable, contradictory, or too vague to interpret, uncertainty itself is a risk signal. Do not treat a missing simulation as evidence that the transaction is harmless; it may simply mean the action is too complex or unsupported to model confidently.

    Finally, size the position according to the uncertainty that remains. A new protocol with limited history, unaudited code, concentrated liquidity, or upgradeable administration may warrant only an amount the user can afford to lose. This is not pessimism. It is a way to keep a single contract failure from becoming a total custody failure. Separating wallets can also reduce blast radius, although it cannot prevent mistakes if the same seed phrase, browser session, or signing habit links them operationally.

    What to watch as wallet integration evolves

    Recent project messaging dated August 24, 2026, emphasizes Rabby Wallet’s support for Ethereum and EVM chains, along with extension access through browsers such as Chrome and Brave. The meaningful development is less the number of supported networks than the challenge it creates: as users move across chains, the wallet must help them distinguish network context, contract identity, token representation, and transaction consequences. Multichain convenience can reduce friction, but it can also increase the chance of sending assets on the wrong network or trusting a familiar-looking dApp in an unfamiliar environment.

    A plausible next phase of wallet design is more useful transaction explanation, not simply more warnings. The strongest systems would help users compare intended action with predicted state change, identify unusual permissions, and make uncertainty visible. That remains conditional on reliable simulation infrastructure and clear protocol metadata. If those inputs are incomplete, a polished warning system could create false confidence—the dangerous belief that everything not flagged has been verified.

    The durable lesson is simple but easy to overlook: the wallet is part of the security boundary, not the whole boundary. Use simulation as a decision aid, approvals as permissions to review, and dApp integration as an ongoing trust relationship rather than a one-click event. The safest DeFi workflow is not the one with the fewest prompts. It is the one in which every important prompt can be understood before a key is used.

    Frequently asked questions

    Does transaction simulation make a DeFi transaction safe?

    No. It can reveal likely balance changes, approvals, and failures before signing, which improves decision quality. But it is based on assumptions about current blockchain state and contract behavior. It cannot guarantee future execution, protocol solvency, honest governance, or protection from every phishing and key-compromise scenario.

    Should I use one wallet for all DeFi activity?

    Using one wallet is convenient but increases concentration risk. A more resilient setup separates long-term holdings from experimental or frequent activity, potentially adding a hardware signer for higher-value assets. The right arrangement depends on the amount at risk, the user’s operational discipline, and how much complexity they can manage without introducing new mistakes.

    What is the most important detail to check before approving a dApp transaction?

    Check the expected state change: what leaves the wallet, what arrives, which contract receives permission, and whether the approval amount is appropriate. If those details do not match the action you intended, stop. A familiar interface or popular protocol name is not a substitute for verifying the actual transaction.

    DeFi dApp Integration Is Not a Connection Problem—It Is a Risk-Interpretation Problem

    A common misconception in decentralized finance is that a wallet is safe once it connects to the right website. In practice, the connection is only the beginning. A decentralized application, or dApp, can request a signature, create token approvals, route a swap through several contracts, or submit a transaction whose final economic effect is difficult to see from a short prompt. The important question is not simply, “Can this wallet connect?” It is, “Can the user understand what the connection and transaction will permit?”

    That distinction matters because DeFi risk sits at the boundary between software and judgment. Smart contracts may execute exactly as written, yet the user may misunderstand what was authorized. A wallet can improve visibility, simulation, and warning signals, but it cannot make an unaudited protocol trustworthy or eliminate every unfamiliar risk. For US-based users managing assets across Ethereum and other EVM-compatible networks, the practical comparison is therefore between different layers of control: basic browser-wallet integration, advanced transaction-aware wallets, and more deliberate operational setups that combine wallet safeguards with independent verification.

    Wallet interface illustrating how transaction details and DeFi contract interactions can be evaluated before signing

    Three approaches to connecting with DeFi protocols

    The simplest approach is a conventional browser wallet that exposes a dApp’s connection request and asks the user to approve signatures. This is convenient and often sufficient for familiar applications, especially when the user understands the network, contract, and asset involved. Its weakness is that convenience can compress a complicated transaction into a generic “confirm” action. The wallet may show a contract address and estimated gas, but those fields do not necessarily explain whether a user is granting spending authority, trading one asset for another, or interacting with a contract that has unexpected logic.

    A second approach is a transaction-aware wallet that adds simulation and contextual risk signals before signing. Simulation attempts to model the likely state changes: which tokens leave the wallet, which assets arrive, whether an approval is created, and whether the transaction is likely to fail. This changes the user’s task from reading raw calldata—a technical encoding of contract instructions—to reviewing an estimated outcome. Tools such as here can be useful in this layer because the wallet becomes an interpretation interface rather than merely a key-management tool.

    The third approach is a high-discipline setup: a separate signing device or hardware wallet for material balances, a smaller active wallet for experimentation, explicit approval management, and manual checks of domains and contract addresses. This offers stronger compartmentalization, but it also introduces friction. A hardware wallet can protect private keys from many malware scenarios while still allowing a user to approve a malicious transaction. Security improves only if the transaction details are understandable on the signing path and the user is willing to stop when the information is unclear.

    These approaches are not mutually exclusive. A user might use a transaction-aware browser wallet for routine DeFi activity, a hardware signer for long-term holdings, and a dedicated test wallet for new protocols. The best design depends on exposure. A small liquidity experiment and a six-figure treasury should not share the same assumptions, even if both use the same blockchain and dApp interface.

    Why simulation helps—and where it can mislead

    Transaction simulation is valuable because it addresses a fundamental asymmetry in DeFi: contracts are deterministic at execution, but the user interface may be ambiguous before execution. If a proposed transaction predicts that a wallet will lose a large amount of a token while receiving nothing meaningful, that is a powerful reason to stop. Likewise, a warning about an unlimited approval can reveal a risk that is easy to miss when a user is focused on a swap or yield opportunity.

    Yet simulation is not a guarantee. It is a forecast under particular assumptions about blockchain state, pricing, block timing, and contract behavior. A transaction may be simulated against one state and executed against another. Market prices can move, liquidity can change, and a contract can depend on information that evolves between signing and inclusion. Some protocols also use upgradeable contracts, external price feeds, callbacks, or complex routing logic that makes the economic outcome harder to summarize completely.

    The boundary condition is especially important for approvals. An approval is not the same as a transfer, but it can give a contract permission to transfer tokens later, subject to the allowance. Revoking unused approvals reduces one attack surface, yet it does not repair a compromised protocol, reverse a completed transaction, or protect a user who signs a new malicious approval. Approval hygiene is risk reduction, not risk elimination.

    There is a related distinction between wallet-level and protocol-level security. A wallet can identify suspicious patterns, flag a risky contract, and make the expected result clearer. It cannot prove that a lending market’s collateral model will remain solvent, that an oracle will remain accurate, or that a bridge’s validators will behave honestly. The wallet helps with authorization risk; it does not fully underwrite economic, governance, liquidity, or smart-contract risk.

    A practical framework for assessing a new dApp

    Before connecting, verify the domain through a trusted route rather than a search advertisement or unsolicited message. Check the intended network and confirm that the dApp’s purpose matches the action being requested. A site that claims to offer a token claim but requests permission to move unrelated assets deserves immediate suspicion.

    Before signing, classify the request. Is it a read-only connection, a message signature, an approval, a swap, a deposit, a withdrawal, or an administrative action? These categories carry different consequences. A message signature may not move funds immediately, but it can still be dangerous when used in phishing systems or off-chain authorization schemes. A token approval may appear routine while creating a future pathway for asset movement.

    Then compare the intended economic result with the simulated result. Look for the assets leaving the wallet, the assets arriving, the spender address, the approval amount, and any unexpected contract calls. If the result is unavailable, contradictory, or too vague to interpret, uncertainty itself is a risk signal. Do not treat a missing simulation as evidence that the transaction is harmless; it may simply mean the action is too complex or unsupported to model confidently.

    Finally, size the position according to the uncertainty that remains. A new protocol with limited history, unaudited code, concentrated liquidity, or upgradeable administration may warrant only an amount the user can afford to lose. This is not pessimism. It is a way to keep a single contract failure from becoming a total custody failure. Separating wallets can also reduce blast radius, although it cannot prevent mistakes if the same seed phrase, browser session, or signing habit links them operationally.

    What to watch as wallet integration evolves

    Recent project messaging dated August 24, 2026, emphasizes Rabby Wallet’s support for Ethereum and EVM chains, along with extension access through browsers such as Chrome and Brave. The meaningful development is less the number of supported networks than the challenge it creates: as users move across chains, the wallet must help them distinguish network context, contract identity, token representation, and transaction consequences. Multichain convenience can reduce friction, but it can also increase the chance of sending assets on the wrong network or trusting a familiar-looking dApp in an unfamiliar environment.

    A plausible next phase of wallet design is more useful transaction explanation, not simply more warnings. The strongest systems would help users compare intended action with predicted state change, identify unusual permissions, and make uncertainty visible. That remains conditional on reliable simulation infrastructure and clear protocol metadata. If those inputs are incomplete, a polished warning system could create false confidence—the dangerous belief that everything not flagged has been verified.

    The durable lesson is simple but easy to overlook: the wallet is part of the security boundary, not the whole boundary. Use simulation as a decision aid, approvals as permissions to review, and dApp integration as an ongoing trust relationship rather than a one-click event. The safest DeFi workflow is not the one with the fewest prompts. It is the one in which every important prompt can be understood before a key is used.

    Frequently asked questions

    Does transaction simulation make a DeFi transaction safe?

    No. It can reveal likely balance changes, approvals, and failures before signing, which improves decision quality. But it is based on assumptions about current blockchain state and contract behavior. It cannot guarantee future execution, protocol solvency, honest governance, or protection from every phishing and key-compromise scenario.

    Should I use one wallet for all DeFi activity?

    Using one wallet is convenient but increases concentration risk. A more resilient setup separates long-term holdings from experimental or frequent activity, potentially adding a hardware signer for higher-value assets. The right arrangement depends on the amount at risk, the user’s operational discipline, and how much complexity they can manage without introducing new mistakes.

    What is the most important detail to check before approving a dApp transaction?

    Check the expected state change: what leaves the wallet, what arrives, which contract receives permission, and whether the approval amount is appropriate. If those details do not match the action you intended, stop. A familiar interface or popular protocol name is not a substitute for verifying the actual transaction.

    DeFi dApp Integration Is Not a Connection Problem—It Is a Risk-Interpretation Problem

    A common misconception in decentralized finance is that a wallet is safe once it connects to the right website. In practice, the connection is only the beginning. A decentralized application, or dApp, can request a signature, create token approvals, route a swap through several contracts, or submit a transaction whose final economic effect is difficult to see from a short prompt. The important question is not simply, “Can this wallet connect?” It is, “Can the user understand what the connection and transaction will permit?”

    That distinction matters because DeFi risk sits at the boundary between software and judgment. Smart contracts may execute exactly as written, yet the user may misunderstand what was authorized. A wallet can improve visibility, simulation, and warning signals, but it cannot make an unaudited protocol trustworthy or eliminate every unfamiliar risk. For US-based users managing assets across Ethereum and other EVM-compatible networks, the practical comparison is therefore between different layers of control: basic browser-wallet integration, advanced transaction-aware wallets, and more deliberate operational setups that combine wallet safeguards with independent verification.

    Wallet interface illustrating how transaction details and DeFi contract interactions can be evaluated before signing

    Three approaches to connecting with DeFi protocols

    The simplest approach is a conventional browser wallet that exposes a dApp’s connection request and asks the user to approve signatures. This is convenient and often sufficient for familiar applications, especially when the user understands the network, contract, and asset involved. Its weakness is that convenience can compress a complicated transaction into a generic “confirm” action. The wallet may show a contract address and estimated gas, but those fields do not necessarily explain whether a user is granting spending authority, trading one asset for another, or interacting with a contract that has unexpected logic.

    A second approach is a transaction-aware wallet that adds simulation and contextual risk signals before signing. Simulation attempts to model the likely state changes: which tokens leave the wallet, which assets arrive, whether an approval is created, and whether the transaction is likely to fail. This changes the user’s task from reading raw calldata—a technical encoding of contract instructions—to reviewing an estimated outcome. Tools such as here can be useful in this layer because the wallet becomes an interpretation interface rather than merely a key-management tool.

    The third approach is a high-discipline setup: a separate signing device or hardware wallet for material balances, a smaller active wallet for experimentation, explicit approval management, and manual checks of domains and contract addresses. This offers stronger compartmentalization, but it also introduces friction. A hardware wallet can protect private keys from many malware scenarios while still allowing a user to approve a malicious transaction. Security improves only if the transaction details are understandable on the signing path and the user is willing to stop when the information is unclear.

    These approaches are not mutually exclusive. A user might use a transaction-aware browser wallet for routine DeFi activity, a hardware signer for long-term holdings, and a dedicated test wallet for new protocols. The best design depends on exposure. A small liquidity experiment and a six-figure treasury should not share the same assumptions, even if both use the same blockchain and dApp interface.

    Why simulation helps—and where it can mislead

    Transaction simulation is valuable because it addresses a fundamental asymmetry in DeFi: contracts are deterministic at execution, but the user interface may be ambiguous before execution. If a proposed transaction predicts that a wallet will lose a large amount of a token while receiving nothing meaningful, that is a powerful reason to stop. Likewise, a warning about an unlimited approval can reveal a risk that is easy to miss when a user is focused on a swap or yield opportunity.

    Yet simulation is not a guarantee. It is a forecast under particular assumptions about blockchain state, pricing, block timing, and contract behavior. A transaction may be simulated against one state and executed against another. Market prices can move, liquidity can change, and a contract can depend on information that evolves between signing and inclusion. Some protocols also use upgradeable contracts, external price feeds, callbacks, or complex routing logic that makes the economic outcome harder to summarize completely.

    The boundary condition is especially important for approvals. An approval is not the same as a transfer, but it can give a contract permission to transfer tokens later, subject to the allowance. Revoking unused approvals reduces one attack surface, yet it does not repair a compromised protocol, reverse a completed transaction, or protect a user who signs a new malicious approval. Approval hygiene is risk reduction, not risk elimination.

    There is a related distinction between wallet-level and protocol-level security. A wallet can identify suspicious patterns, flag a risky contract, and make the expected result clearer. It cannot prove that a lending market’s collateral model will remain solvent, that an oracle will remain accurate, or that a bridge’s validators will behave honestly. The wallet helps with authorization risk; it does not fully underwrite economic, governance, liquidity, or smart-contract risk.

    A practical framework for assessing a new dApp

    Before connecting, verify the domain through a trusted route rather than a search advertisement or unsolicited message. Check the intended network and confirm that the dApp’s purpose matches the action being requested. A site that claims to offer a token claim but requests permission to move unrelated assets deserves immediate suspicion.

    Before signing, classify the request. Is it a read-only connection, a message signature, an approval, a swap, a deposit, a withdrawal, or an administrative action? These categories carry different consequences. A message signature may not move funds immediately, but it can still be dangerous when used in phishing systems or off-chain authorization schemes. A token approval may appear routine while creating a future pathway for asset movement.

    Then compare the intended economic result with the simulated result. Look for the assets leaving the wallet, the assets arriving, the spender address, the approval amount, and any unexpected contract calls. If the result is unavailable, contradictory, or too vague to interpret, uncertainty itself is a risk signal. Do not treat a missing simulation as evidence that the transaction is harmless; it may simply mean the action is too complex or unsupported to model confidently.

    Finally, size the position according to the uncertainty that remains. A new protocol with limited history, unaudited code, concentrated liquidity, or upgradeable administration may warrant only an amount the user can afford to lose. This is not pessimism. It is a way to keep a single contract failure from becoming a total custody failure. Separating wallets can also reduce blast radius, although it cannot prevent mistakes if the same seed phrase, browser session, or signing habit links them operationally.

    What to watch as wallet integration evolves

    Recent project messaging dated August 24, 2026, emphasizes Rabby Wallet’s support for Ethereum and EVM chains, along with extension access through browsers such as Chrome and Brave. The meaningful development is less the number of supported networks than the challenge it creates: as users move across chains, the wallet must help them distinguish network context, contract identity, token representation, and transaction consequences. Multichain convenience can reduce friction, but it can also increase the chance of sending assets on the wrong network or trusting a familiar-looking dApp in an unfamiliar environment.

    A plausible next phase of wallet design is more useful transaction explanation, not simply more warnings. The strongest systems would help users compare intended action with predicted state change, identify unusual permissions, and make uncertainty visible. That remains conditional on reliable simulation infrastructure and clear protocol metadata. If those inputs are incomplete, a polished warning system could create false confidence—the dangerous belief that everything not flagged has been verified.

    The durable lesson is simple but easy to overlook: the wallet is part of the security boundary, not the whole boundary. Use simulation as a decision aid, approvals as permissions to review, and dApp integration as an ongoing trust relationship rather than a one-click event. The safest DeFi workflow is not the one with the fewest prompts. It is the one in which every important prompt can be understood before a key is used.

    Frequently asked questions

    Does transaction simulation make a DeFi transaction safe?

    No. It can reveal likely balance changes, approvals, and failures before signing, which improves decision quality. But it is based on assumptions about current blockchain state and contract behavior. It cannot guarantee future execution, protocol solvency, honest governance, or protection from every phishing and key-compromise scenario.

    Should I use one wallet for all DeFi activity?

    Using one wallet is convenient but increases concentration risk. A more resilient setup separates long-term holdings from experimental or frequent activity, potentially adding a hardware signer for higher-value assets. The right arrangement depends on the amount at risk, the user’s operational discipline, and how much complexity they can manage without introducing new mistakes.

    What is the most important detail to check before approving a dApp transaction?

    Check the expected state change: what leaves the wallet, what arrives, which contract receives permission, and whether the approval amount is appropriate. If those details do not match the action you intended, stop. A familiar interface or popular protocol name is not a substitute for verifying the actual transaction.

    DeFi dApp Integration Is Not a Connection Problem—It Is a Risk-Interpretation Problem

    A common misconception in decentralized finance is that a wallet is safe once it connects to the right website. In practice, the connection is only the beginning. A decentralized application, or dApp, can request a signature, create token approvals, route a swap through several contracts, or submit a transaction whose final economic effect is difficult to see from a short prompt. The important question is not simply, “Can this wallet connect?” It is, “Can the user understand what the connection and transaction will permit?”

    That distinction matters because DeFi risk sits at the boundary between software and judgment. Smart contracts may execute exactly as written, yet the user may misunderstand what was authorized. A wallet can improve visibility, simulation, and warning signals, but it cannot make an unaudited protocol trustworthy or eliminate every unfamiliar risk. For US-based users managing assets across Ethereum and other EVM-compatible networks, the practical comparison is therefore between different layers of control: basic browser-wallet integration, advanced transaction-aware wallets, and more deliberate operational setups that combine wallet safeguards with independent verification.

    Wallet interface illustrating how transaction details and DeFi contract interactions can be evaluated before signing

    Three approaches to connecting with DeFi protocols

    The simplest approach is a conventional browser wallet that exposes a dApp’s connection request and asks the user to approve signatures. This is convenient and often sufficient for familiar applications, especially when the user understands the network, contract, and asset involved. Its weakness is that convenience can compress a complicated transaction into a generic “confirm” action. The wallet may show a contract address and estimated gas, but those fields do not necessarily explain whether a user is granting spending authority, trading one asset for another, or interacting with a contract that has unexpected logic.

    A second approach is a transaction-aware wallet that adds simulation and contextual risk signals before signing. Simulation attempts to model the likely state changes: which tokens leave the wallet, which assets arrive, whether an approval is created, and whether the transaction is likely to fail. This changes the user’s task from reading raw calldata—a technical encoding of contract instructions—to reviewing an estimated outcome. Tools such as here can be useful in this layer because the wallet becomes an interpretation interface rather than merely a key-management tool.

    The third approach is a high-discipline setup: a separate signing device or hardware wallet for material balances, a smaller active wallet for experimentation, explicit approval management, and manual checks of domains and contract addresses. This offers stronger compartmentalization, but it also introduces friction. A hardware wallet can protect private keys from many malware scenarios while still allowing a user to approve a malicious transaction. Security improves only if the transaction details are understandable on the signing path and the user is willing to stop when the information is unclear.

    These approaches are not mutually exclusive. A user might use a transaction-aware browser wallet for routine DeFi activity, a hardware signer for long-term holdings, and a dedicated test wallet for new protocols. The best design depends on exposure. A small liquidity experiment and a six-figure treasury should not share the same assumptions, even if both use the same blockchain and dApp interface.

    Why simulation helps—and where it can mislead

    Transaction simulation is valuable because it addresses a fundamental asymmetry in DeFi: contracts are deterministic at execution, but the user interface may be ambiguous before execution. If a proposed transaction predicts that a wallet will lose a large amount of a token while receiving nothing meaningful, that is a powerful reason to stop. Likewise, a warning about an unlimited approval can reveal a risk that is easy to miss when a user is focused on a swap or yield opportunity.

    Yet simulation is not a guarantee. It is a forecast under particular assumptions about blockchain state, pricing, block timing, and contract behavior. A transaction may be simulated against one state and executed against another. Market prices can move, liquidity can change, and a contract can depend on information that evolves between signing and inclusion. Some protocols also use upgradeable contracts, external price feeds, callbacks, or complex routing logic that makes the economic outcome harder to summarize completely.

    The boundary condition is especially important for approvals. An approval is not the same as a transfer, but it can give a contract permission to transfer tokens later, subject to the allowance. Revoking unused approvals reduces one attack surface, yet it does not repair a compromised protocol, reverse a completed transaction, or protect a user who signs a new malicious approval. Approval hygiene is risk reduction, not risk elimination.

    There is a related distinction between wallet-level and protocol-level security. A wallet can identify suspicious patterns, flag a risky contract, and make the expected result clearer. It cannot prove that a lending market’s collateral model will remain solvent, that an oracle will remain accurate, or that a bridge’s validators will behave honestly. The wallet helps with authorization risk; it does not fully underwrite economic, governance, liquidity, or smart-contract risk.

    A practical framework for assessing a new dApp

    Before connecting, verify the domain through a trusted route rather than a search advertisement or unsolicited message. Check the intended network and confirm that the dApp’s purpose matches the action being requested. A site that claims to offer a token claim but requests permission to move unrelated assets deserves immediate suspicion.

    Before signing, classify the request. Is it a read-only connection, a message signature, an approval, a swap, a deposit, a withdrawal, or an administrative action? These categories carry different consequences. A message signature may not move funds immediately, but it can still be dangerous when used in phishing systems or off-chain authorization schemes. A token approval may appear routine while creating a future pathway for asset movement.

    Then compare the intended economic result with the simulated result. Look for the assets leaving the wallet, the assets arriving, the spender address, the approval amount, and any unexpected contract calls. If the result is unavailable, contradictory, or too vague to interpret, uncertainty itself is a risk signal. Do not treat a missing simulation as evidence that the transaction is harmless; it may simply mean the action is too complex or unsupported to model confidently.

    Finally, size the position according to the uncertainty that remains. A new protocol with limited history, unaudited code, concentrated liquidity, or upgradeable administration may warrant only an amount the user can afford to lose. This is not pessimism. It is a way to keep a single contract failure from becoming a total custody failure. Separating wallets can also reduce blast radius, although it cannot prevent mistakes if the same seed phrase, browser session, or signing habit links them operationally.

    What to watch as wallet integration evolves

    Recent project messaging dated August 24, 2026, emphasizes Rabby Wallet’s support for Ethereum and EVM chains, along with extension access through browsers such as Chrome and Brave. The meaningful development is less the number of supported networks than the challenge it creates: as users move across chains, the wallet must help them distinguish network context, contract identity, token representation, and transaction consequences. Multichain convenience can reduce friction, but it can also increase the chance of sending assets on the wrong network or trusting a familiar-looking dApp in an unfamiliar environment.

    A plausible next phase of wallet design is more useful transaction explanation, not simply more warnings. The strongest systems would help users compare intended action with predicted state change, identify unusual permissions, and make uncertainty visible. That remains conditional on reliable simulation infrastructure and clear protocol metadata. If those inputs are incomplete, a polished warning system could create false confidence—the dangerous belief that everything not flagged has been verified.

    The durable lesson is simple but easy to overlook: the wallet is part of the security boundary, not the whole boundary. Use simulation as a decision aid, approvals as permissions to review, and dApp integration as an ongoing trust relationship rather than a one-click event. The safest DeFi workflow is not the one with the fewest prompts. It is the one in which every important prompt can be understood before a key is used.

    Frequently asked questions

    Does transaction simulation make a DeFi transaction safe?

    No. It can reveal likely balance changes, approvals, and failures before signing, which improves decision quality. But it is based on assumptions about current blockchain state and contract behavior. It cannot guarantee future execution, protocol solvency, honest governance, or protection from every phishing and key-compromise scenario.

    Should I use one wallet for all DeFi activity?

    Using one wallet is convenient but increases concentration risk. A more resilient setup separates long-term holdings from experimental or frequent activity, potentially adding a hardware signer for higher-value assets. The right arrangement depends on the amount at risk, the user’s operational discipline, and how much complexity they can manage without introducing new mistakes.

    What is the most important detail to check before approving a dApp transaction?

    Check the expected state change: what leaves the wallet, what arrives, which contract receives permission, and whether the approval amount is appropriate. If those details do not match the action you intended, stop. A familiar interface or popular protocol name is not a substitute for verifying the actual transaction.

    DeFi dApp Integration Is Not a Connection Problem—It Is a Risk-Interpretation Problem

    A common misconception in decentralized finance is that a wallet is safe once it connects to the right website. In practice, the connection is only the beginning. A decentralized application, or dApp, can request a signature, create token approvals, route a swap through several contracts, or submit a transaction whose final economic effect is difficult to see from a short prompt. The important question is not simply, “Can this wallet connect?” It is, “Can the user understand what the connection and transaction will permit?”

    That distinction matters because DeFi risk sits at the boundary between software and judgment. Smart contracts may execute exactly as written, yet the user may misunderstand what was authorized. A wallet can improve visibility, simulation, and warning signals, but it cannot make an unaudited protocol trustworthy or eliminate every unfamiliar risk. For US-based users managing assets across Ethereum and other EVM-compatible networks, the practical comparison is therefore between different layers of control: basic browser-wallet integration, advanced transaction-aware wallets, and more deliberate operational setups that combine wallet safeguards with independent verification.

    Wallet interface illustrating how transaction details and DeFi contract interactions can be evaluated before signing

    Three approaches to connecting with DeFi protocols

    The simplest approach is a conventional browser wallet that exposes a dApp’s connection request and asks the user to approve signatures. This is convenient and often sufficient for familiar applications, especially when the user understands the network, contract, and asset involved. Its weakness is that convenience can compress a complicated transaction into a generic “confirm” action. The wallet may show a contract address and estimated gas, but those fields do not necessarily explain whether a user is granting spending authority, trading one asset for another, or interacting with a contract that has unexpected logic.

    A second approach is a transaction-aware wallet that adds simulation and contextual risk signals before signing. Simulation attempts to model the likely state changes: which tokens leave the wallet, which assets arrive, whether an approval is created, and whether the transaction is likely to fail. This changes the user’s task from reading raw calldata—a technical encoding of contract instructions—to reviewing an estimated outcome. Tools such as here can be useful in this layer because the wallet becomes an interpretation interface rather than merely a key-management tool.

    The third approach is a high-discipline setup: a separate signing device or hardware wallet for material balances, a smaller active wallet for experimentation, explicit approval management, and manual checks of domains and contract addresses. This offers stronger compartmentalization, but it also introduces friction. A hardware wallet can protect private keys from many malware scenarios while still allowing a user to approve a malicious transaction. Security improves only if the transaction details are understandable on the signing path and the user is willing to stop when the information is unclear.

    These approaches are not mutually exclusive. A user might use a transaction-aware browser wallet for routine DeFi activity, a hardware signer for long-term holdings, and a dedicated test wallet for new protocols. The best design depends on exposure. A small liquidity experiment and a six-figure treasury should not share the same assumptions, even if both use the same blockchain and dApp interface.

    Why simulation helps—and where it can mislead

    Transaction simulation is valuable because it addresses a fundamental asymmetry in DeFi: contracts are deterministic at execution, but the user interface may be ambiguous before execution. If a proposed transaction predicts that a wallet will lose a large amount of a token while receiving nothing meaningful, that is a powerful reason to stop. Likewise, a warning about an unlimited approval can reveal a risk that is easy to miss when a user is focused on a swap or yield opportunity.

    Yet simulation is not a guarantee. It is a forecast under particular assumptions about blockchain state, pricing, block timing, and contract behavior. A transaction may be simulated against one state and executed against another. Market prices can move, liquidity can change, and a contract can depend on information that evolves between signing and inclusion. Some protocols also use upgradeable contracts, external price feeds, callbacks, or complex routing logic that makes the economic outcome harder to summarize completely.

    The boundary condition is especially important for approvals. An approval is not the same as a transfer, but it can give a contract permission to transfer tokens later, subject to the allowance. Revoking unused approvals reduces one attack surface, yet it does not repair a compromised protocol, reverse a completed transaction, or protect a user who signs a new malicious approval. Approval hygiene is risk reduction, not risk elimination.

    There is a related distinction between wallet-level and protocol-level security. A wallet can identify suspicious patterns, flag a risky contract, and make the expected result clearer. It cannot prove that a lending market’s collateral model will remain solvent, that an oracle will remain accurate, or that a bridge’s validators will behave honestly. The wallet helps with authorization risk; it does not fully underwrite economic, governance, liquidity, or smart-contract risk.

    A practical framework for assessing a new dApp

    Before connecting, verify the domain through a trusted route rather than a search advertisement or unsolicited message. Check the intended network and confirm that the dApp’s purpose matches the action being requested. A site that claims to offer a token claim but requests permission to move unrelated assets deserves immediate suspicion.

    Before signing, classify the request. Is it a read-only connection, a message signature, an approval, a swap, a deposit, a withdrawal, or an administrative action? These categories carry different consequences. A message signature may not move funds immediately, but it can still be dangerous when used in phishing systems or off-chain authorization schemes. A token approval may appear routine while creating a future pathway for asset movement.

    Then compare the intended economic result with the simulated result. Look for the assets leaving the wallet, the assets arriving, the spender address, the approval amount, and any unexpected contract calls. If the result is unavailable, contradictory, or too vague to interpret, uncertainty itself is a risk signal. Do not treat a missing simulation as evidence that the transaction is harmless; it may simply mean the action is too complex or unsupported to model confidently.

    Finally, size the position according to the uncertainty that remains. A new protocol with limited history, unaudited code, concentrated liquidity, or upgradeable administration may warrant only an amount the user can afford to lose. This is not pessimism. It is a way to keep a single contract failure from becoming a total custody failure. Separating wallets can also reduce blast radius, although it cannot prevent mistakes if the same seed phrase, browser session, or signing habit links them operationally.

    What to watch as wallet integration evolves

    Recent project messaging dated August 24, 2026, emphasizes Rabby Wallet’s support for Ethereum and EVM chains, along with extension access through browsers such as Chrome and Brave. The meaningful development is less the number of supported networks than the challenge it creates: as users move across chains, the wallet must help them distinguish network context, contract identity, token representation, and transaction consequences. Multichain convenience can reduce friction, but it can also increase the chance of sending assets on the wrong network or trusting a familiar-looking dApp in an unfamiliar environment.

    A plausible next phase of wallet design is more useful transaction explanation, not simply more warnings. The strongest systems would help users compare intended action with predicted state change, identify unusual permissions, and make uncertainty visible. That remains conditional on reliable simulation infrastructure and clear protocol metadata. If those inputs are incomplete, a polished warning system could create false confidence—the dangerous belief that everything not flagged has been verified.

    The durable lesson is simple but easy to overlook: the wallet is part of the security boundary, not the whole boundary. Use simulation as a decision aid, approvals as permissions to review, and dApp integration as an ongoing trust relationship rather than a one-click event. The safest DeFi workflow is not the one with the fewest prompts. It is the one in which every important prompt can be understood before a key is used.

    Frequently asked questions

    Does transaction simulation make a DeFi transaction safe?

    No. It can reveal likely balance changes, approvals, and failures before signing, which improves decision quality. But it is based on assumptions about current blockchain state and contract behavior. It cannot guarantee future execution, protocol solvency, honest governance, or protection from every phishing and key-compromise scenario.

    Should I use one wallet for all DeFi activity?

    Using one wallet is convenient but increases concentration risk. A more resilient setup separates long-term holdings from experimental or frequent activity, potentially adding a hardware signer for higher-value assets. The right arrangement depends on the amount at risk, the user’s operational discipline, and how much complexity they can manage without introducing new mistakes.

    What is the most important detail to check before approving a dApp transaction?

    Check the expected state change: what leaves the wallet, what arrives, which contract receives permission, and whether the approval amount is appropriate. If those details do not match the action you intended, stop. A familiar interface or popular protocol name is not a substitute for verifying the actual transaction.

    DeFi dApp Integration Is Not a Connection Problem—It Is a Risk-Interpretation Problem

    A common misconception in decentralized finance is that a wallet is safe once it connects to the right website. In practice, the connection is only the beginning. A decentralized application, or dApp, can request a signature, create token approvals, route a swap through several contracts, or submit a transaction whose final economic effect is difficult to see from a short prompt. The important question is not simply, “Can this wallet connect?” It is, “Can the user understand what the connection and transaction will permit?”

    That distinction matters because DeFi risk sits at the boundary between software and judgment. Smart contracts may execute exactly as written, yet the user may misunderstand what was authorized. A wallet can improve visibility, simulation, and warning signals, but it cannot make an unaudited protocol trustworthy or eliminate every unfamiliar risk. For US-based users managing assets across Ethereum and other EVM-compatible networks, the practical comparison is therefore between different layers of control: basic browser-wallet integration, advanced transaction-aware wallets, and more deliberate operational setups that combine wallet safeguards with independent verification.

    Wallet interface illustrating how transaction details and DeFi contract interactions can be evaluated before signing

    Three approaches to connecting with DeFi protocols

    The simplest approach is a conventional browser wallet that exposes a dApp’s connection request and asks the user to approve signatures. This is convenient and often sufficient for familiar applications, especially when the user understands the network, contract, and asset involved. Its weakness is that convenience can compress a complicated transaction into a generic “confirm” action. The wallet may show a contract address and estimated gas, but those fields do not necessarily explain whether a user is granting spending authority, trading one asset for another, or interacting with a contract that has unexpected logic.

    A second approach is a transaction-aware wallet that adds simulation and contextual risk signals before signing. Simulation attempts to model the likely state changes: which tokens leave the wallet, which assets arrive, whether an approval is created, and whether the transaction is likely to fail. This changes the user’s task from reading raw calldata—a technical encoding of contract instructions—to reviewing an estimated outcome. Tools such as here can be useful in this layer because the wallet becomes an interpretation interface rather than merely a key-management tool.

    The third approach is a high-discipline setup: a separate signing device or hardware wallet for material balances, a smaller active wallet for experimentation, explicit approval management, and manual checks of domains and contract addresses. This offers stronger compartmentalization, but it also introduces friction. A hardware wallet can protect private keys from many malware scenarios while still allowing a user to approve a malicious transaction. Security improves only if the transaction details are understandable on the signing path and the user is willing to stop when the information is unclear.

    These approaches are not mutually exclusive. A user might use a transaction-aware browser wallet for routine DeFi activity, a hardware signer for long-term holdings, and a dedicated test wallet for new protocols. The best design depends on exposure. A small liquidity experiment and a six-figure treasury should not share the same assumptions, even if both use the same blockchain and dApp interface.

    Why simulation helps—and where it can mislead

    Transaction simulation is valuable because it addresses a fundamental asymmetry in DeFi: contracts are deterministic at execution, but the user interface may be ambiguous before execution. If a proposed transaction predicts that a wallet will lose a large amount of a token while receiving nothing meaningful, that is a powerful reason to stop. Likewise, a warning about an unlimited approval can reveal a risk that is easy to miss when a user is focused on a swap or yield opportunity.

    Yet simulation is not a guarantee. It is a forecast under particular assumptions about blockchain state, pricing, block timing, and contract behavior. A transaction may be simulated against one state and executed against another. Market prices can move, liquidity can change, and a contract can depend on information that evolves between signing and inclusion. Some protocols also use upgradeable contracts, external price feeds, callbacks, or complex routing logic that makes the economic outcome harder to summarize completely.

    The boundary condition is especially important for approvals. An approval is not the same as a transfer, but it can give a contract permission to transfer tokens later, subject to the allowance. Revoking unused approvals reduces one attack surface, yet it does not repair a compromised protocol, reverse a completed transaction, or protect a user who signs a new malicious approval. Approval hygiene is risk reduction, not risk elimination.

    There is a related distinction between wallet-level and protocol-level security. A wallet can identify suspicious patterns, flag a risky contract, and make the expected result clearer. It cannot prove that a lending market’s collateral model will remain solvent, that an oracle will remain accurate, or that a bridge’s validators will behave honestly. The wallet helps with authorization risk; it does not fully underwrite economic, governance, liquidity, or smart-contract risk.

    A practical framework for assessing a new dApp

    Before connecting, verify the domain through a trusted route rather than a search advertisement or unsolicited message. Check the intended network and confirm that the dApp’s purpose matches the action being requested. A site that claims to offer a token claim but requests permission to move unrelated assets deserves immediate suspicion.

    Before signing, classify the request. Is it a read-only connection, a message signature, an approval, a swap, a deposit, a withdrawal, or an administrative action? These categories carry different consequences. A message signature may not move funds immediately, but it can still be dangerous when used in phishing systems or off-chain authorization schemes. A token approval may appear routine while creating a future pathway for asset movement.

    Then compare the intended economic result with the simulated result. Look for the assets leaving the wallet, the assets arriving, the spender address, the approval amount, and any unexpected contract calls. If the result is unavailable, contradictory, or too vague to interpret, uncertainty itself is a risk signal. Do not treat a missing simulation as evidence that the transaction is harmless; it may simply mean the action is too complex or unsupported to model confidently.

    Finally, size the position according to the uncertainty that remains. A new protocol with limited history, unaudited code, concentrated liquidity, or upgradeable administration may warrant only an amount the user can afford to lose. This is not pessimism. It is a way to keep a single contract failure from becoming a total custody failure. Separating wallets can also reduce blast radius, although it cannot prevent mistakes if the same seed phrase, browser session, or signing habit links them operationally.

    What to watch as wallet integration evolves

    Recent project messaging dated August 24, 2026, emphasizes Rabby Wallet’s support for Ethereum and EVM chains, along with extension access through browsers such as Chrome and Brave. The meaningful development is less the number of supported networks than the challenge it creates: as users move across chains, the wallet must help them distinguish network context, contract identity, token representation, and transaction consequences. Multichain convenience can reduce friction, but it can also increase the chance of sending assets on the wrong network or trusting a familiar-looking dApp in an unfamiliar environment.

    A plausible next phase of wallet design is more useful transaction explanation, not simply more warnings. The strongest systems would help users compare intended action with predicted state change, identify unusual permissions, and make uncertainty visible. That remains conditional on reliable simulation infrastructure and clear protocol metadata. If those inputs are incomplete, a polished warning system could create false confidence—the dangerous belief that everything not flagged has been verified.

    The durable lesson is simple but easy to overlook: the wallet is part of the security boundary, not the whole boundary. Use simulation as a decision aid, approvals as permissions to review, and dApp integration as an ongoing trust relationship rather than a one-click event. The safest DeFi workflow is not the one with the fewest prompts. It is the one in which every important prompt can be understood before a key is used.

    Frequently asked questions

    Does transaction simulation make a DeFi transaction safe?

    No. It can reveal likely balance changes, approvals, and failures before signing, which improves decision quality. But it is based on assumptions about current blockchain state and contract behavior. It cannot guarantee future execution, protocol solvency, honest governance, or protection from every phishing and key-compromise scenario.

    Should I use one wallet for all DeFi activity?

    Using one wallet is convenient but increases concentration risk. A more resilient setup separates long-term holdings from experimental or frequent activity, potentially adding a hardware signer for higher-value assets. The right arrangement depends on the amount at risk, the user’s operational discipline, and how much complexity they can manage without introducing new mistakes.

    What is the most important detail to check before approving a dApp transaction?

    Check the expected state change: what leaves the wallet, what arrives, which contract receives permission, and whether the approval amount is appropriate. If those details do not match the action you intended, stop. A familiar interface or popular protocol name is not a substitute for verifying the actual transaction.

    DeFi dApp Integration Is Not a Connection Problem—It Is a Risk-Interpretation Problem

    A common misconception in decentralized finance is that a wallet is safe once it connects to the right website. In practice, the connection is only the beginning. A decentralized application, or dApp, can request a signature, create token approvals, route a swap through several contracts, or submit a transaction whose final economic effect is difficult to see from a short prompt. The important question is not simply, “Can this wallet connect?” It is, “Can the user understand what the connection and transaction will permit?”

    That distinction matters because DeFi risk sits at the boundary between software and judgment. Smart contracts may execute exactly as written, yet the user may misunderstand what was authorized. A wallet can improve visibility, simulation, and warning signals, but it cannot make an unaudited protocol trustworthy or eliminate every unfamiliar risk. For US-based users managing assets across Ethereum and other EVM-compatible networks, the practical comparison is therefore between different layers of control: basic browser-wallet integration, advanced transaction-aware wallets, and more deliberate operational setups that combine wallet safeguards with independent verification.

    Wallet interface illustrating how transaction details and DeFi contract interactions can be evaluated before signing

    Three approaches to connecting with DeFi protocols

    The simplest approach is a conventional browser wallet that exposes a dApp’s connection request and asks the user to approve signatures. This is convenient and often sufficient for familiar applications, especially when the user understands the network, contract, and asset involved. Its weakness is that convenience can compress a complicated transaction into a generic “confirm” action. The wallet may show a contract address and estimated gas, but those fields do not necessarily explain whether a user is granting spending authority, trading one asset for another, or interacting with a contract that has unexpected logic.

    A second approach is a transaction-aware wallet that adds simulation and contextual risk signals before signing. Simulation attempts to model the likely state changes: which tokens leave the wallet, which assets arrive, whether an approval is created, and whether the transaction is likely to fail. This changes the user’s task from reading raw calldata—a technical encoding of contract instructions—to reviewing an estimated outcome. Tools such as here can be useful in this layer because the wallet becomes an interpretation interface rather than merely a key-management tool.

    The third approach is a high-discipline setup: a separate signing device or hardware wallet for material balances, a smaller active wallet for experimentation, explicit approval management, and manual checks of domains and contract addresses. This offers stronger compartmentalization, but it also introduces friction. A hardware wallet can protect private keys from many malware scenarios while still allowing a user to approve a malicious transaction. Security improves only if the transaction details are understandable on the signing path and the user is willing to stop when the information is unclear.

    These approaches are not mutually exclusive. A user might use a transaction-aware browser wallet for routine DeFi activity, a hardware signer for long-term holdings, and a dedicated test wallet for new protocols. The best design depends on exposure. A small liquidity experiment and a six-figure treasury should not share the same assumptions, even if both use the same blockchain and dApp interface.

    Why simulation helps—and where it can mislead

    Transaction simulation is valuable because it addresses a fundamental asymmetry in DeFi: contracts are deterministic at execution, but the user interface may be ambiguous before execution. If a proposed transaction predicts that a wallet will lose a large amount of a token while receiving nothing meaningful, that is a powerful reason to stop. Likewise, a warning about an unlimited approval can reveal a risk that is easy to miss when a user is focused on a swap or yield opportunity.

    Yet simulation is not a guarantee. It is a forecast under particular assumptions about blockchain state, pricing, block timing, and contract behavior. A transaction may be simulated against one state and executed against another. Market prices can move, liquidity can change, and a contract can depend on information that evolves between signing and inclusion. Some protocols also use upgradeable contracts, external price feeds, callbacks, or complex routing logic that makes the economic outcome harder to summarize completely.

    The boundary condition is especially important for approvals. An approval is not the same as a transfer, but it can give a contract permission to transfer tokens later, subject to the allowance. Revoking unused approvals reduces one attack surface, yet it does not repair a compromised protocol, reverse a completed transaction, or protect a user who signs a new malicious approval. Approval hygiene is risk reduction, not risk elimination.

    There is a related distinction between wallet-level and protocol-level security. A wallet can identify suspicious patterns, flag a risky contract, and make the expected result clearer. It cannot prove that a lending market’s collateral model will remain solvent, that an oracle will remain accurate, or that a bridge’s validators will behave honestly. The wallet helps with authorization risk; it does not fully underwrite economic, governance, liquidity, or smart-contract risk.

    A practical framework for assessing a new dApp

    Before connecting, verify the domain through a trusted route rather than a search advertisement or unsolicited message. Check the intended network and confirm that the dApp’s purpose matches the action being requested. A site that claims to offer a token claim but requests permission to move unrelated assets deserves immediate suspicion.

    Before signing, classify the request. Is it a read-only connection, a message signature, an approval, a swap, a deposit, a withdrawal, or an administrative action? These categories carry different consequences. A message signature may not move funds immediately, but it can still be dangerous when used in phishing systems or off-chain authorization schemes. A token approval may appear routine while creating a future pathway for asset movement.

    Then compare the intended economic result with the simulated result. Look for the assets leaving the wallet, the assets arriving, the spender address, the approval amount, and any unexpected contract calls. If the result is unavailable, contradictory, or too vague to interpret, uncertainty itself is a risk signal. Do not treat a missing simulation as evidence that the transaction is harmless; it may simply mean the action is too complex or unsupported to model confidently.

    Finally, size the position according to the uncertainty that remains. A new protocol with limited history, unaudited code, concentrated liquidity, or upgradeable administration may warrant only an amount the user can afford to lose. This is not pessimism. It is a way to keep a single contract failure from becoming a total custody failure. Separating wallets can also reduce blast radius, although it cannot prevent mistakes if the same seed phrase, browser session, or signing habit links them operationally.

    What to watch as wallet integration evolves

    Recent project messaging dated August 24, 2026, emphasizes Rabby Wallet’s support for Ethereum and EVM chains, along with extension access through browsers such as Chrome and Brave. The meaningful development is less the number of supported networks than the challenge it creates: as users move across chains, the wallet must help them distinguish network context, contract identity, token representation, and transaction consequences. Multichain convenience can reduce friction, but it can also increase the chance of sending assets on the wrong network or trusting a familiar-looking dApp in an unfamiliar environment.

    A plausible next phase of wallet design is more useful transaction explanation, not simply more warnings. The strongest systems would help users compare intended action with predicted state change, identify unusual permissions, and make uncertainty visible. That remains conditional on reliable simulation infrastructure and clear protocol metadata. If those inputs are incomplete, a polished warning system could create false confidence—the dangerous belief that everything not flagged has been verified.

    The durable lesson is simple but easy to overlook: the wallet is part of the security boundary, not the whole boundary. Use simulation as a decision aid, approvals as permissions to review, and dApp integration as an ongoing trust relationship rather than a one-click event. The safest DeFi workflow is not the one with the fewest prompts. It is the one in which every important prompt can be understood before a key is used.

    Frequently asked questions

    Does transaction simulation make a DeFi transaction safe?

    No. It can reveal likely balance changes, approvals, and failures before signing, which improves decision quality. But it is based on assumptions about current blockchain state and contract behavior. It cannot guarantee future execution, protocol solvency, honest governance, or protection from every phishing and key-compromise scenario.

    Should I use one wallet for all DeFi activity?

    Using one wallet is convenient but increases concentration risk. A more resilient setup separates long-term holdings from experimental or frequent activity, potentially adding a hardware signer for higher-value assets. The right arrangement depends on the amount at risk, the user’s operational discipline, and how much complexity they can manage without introducing new mistakes.

    What is the most important detail to check before approving a dApp transaction?

    Check the expected state change: what leaves the wallet, what arrives, which contract receives permission, and whether the approval amount is appropriate. If those details do not match the action you intended, stop. A familiar interface or popular protocol name is not a substitute for verifying the actual transaction.

    DeFi dApp Integration Is Not a Connection Problem—It Is a Risk-Interpretation Problem

    A common misconception in decentralized finance is that a wallet is safe once it connects to the right website. In practice, the connection is only the beginning. A decentralized application, or dApp, can request a signature, create token approvals, route a swap through several contracts, or submit a transaction whose final economic effect is difficult to see from a short prompt. The important question is not simply, “Can this wallet connect?” It is, “Can the user understand what the connection and transaction will permit?”

    That distinction matters because DeFi risk sits at the boundary between software and judgment. Smart contracts may execute exactly as written, yet the user may misunderstand what was authorized. A wallet can improve visibility, simulation, and warning signals, but it cannot make an unaudited protocol trustworthy or eliminate every unfamiliar risk. For US-based users managing assets across Ethereum and other EVM-compatible networks, the practical comparison is therefore between different layers of control: basic browser-wallet integration, advanced transaction-aware wallets, and more deliberate operational setups that combine wallet safeguards with independent verification.

    Wallet interface illustrating how transaction details and DeFi contract interactions can be evaluated before signing

    Three approaches to connecting with DeFi protocols

    The simplest approach is a conventional browser wallet that exposes a dApp’s connection request and asks the user to approve signatures. This is convenient and often sufficient for familiar applications, especially when the user understands the network, contract, and asset involved. Its weakness is that convenience can compress a complicated transaction into a generic “confirm” action. The wallet may show a contract address and estimated gas, but those fields do not necessarily explain whether a user is granting spending authority, trading one asset for another, or interacting with a contract that has unexpected logic.

    A second approach is a transaction-aware wallet that adds simulation and contextual risk signals before signing. Simulation attempts to model the likely state changes: which tokens leave the wallet, which assets arrive, whether an approval is created, and whether the transaction is likely to fail. This changes the user’s task from reading raw calldata—a technical encoding of contract instructions—to reviewing an estimated outcome. Tools such as here can be useful in this layer because the wallet becomes an interpretation interface rather than merely a key-management tool.

    The third approach is a high-discipline setup: a separate signing device or hardware wallet for material balances, a smaller active wallet for experimentation, explicit approval management, and manual checks of domains and contract addresses. This offers stronger compartmentalization, but it also introduces friction. A hardware wallet can protect private keys from many malware scenarios while still allowing a user to approve a malicious transaction. Security improves only if the transaction details are understandable on the signing path and the user is willing to stop when the information is unclear.

    These approaches are not mutually exclusive. A user might use a transaction-aware browser wallet for routine DeFi activity, a hardware signer for long-term holdings, and a dedicated test wallet for new protocols. The best design depends on exposure. A small liquidity experiment and a six-figure treasury should not share the same assumptions, even if both use the same blockchain and dApp interface.

    Why simulation helps—and where it can mislead

    Transaction simulation is valuable because it addresses a fundamental asymmetry in DeFi: contracts are deterministic at execution, but the user interface may be ambiguous before execution. If a proposed transaction predicts that a wallet will lose a large amount of a token while receiving nothing meaningful, that is a powerful reason to stop. Likewise, a warning about an unlimited approval can reveal a risk that is easy to miss when a user is focused on a swap or yield opportunity.

    Yet simulation is not a guarantee. It is a forecast under particular assumptions about blockchain state, pricing, block timing, and contract behavior. A transaction may be simulated against one state and executed against another. Market prices can move, liquidity can change, and a contract can depend on information that evolves between signing and inclusion. Some protocols also use upgradeable contracts, external price feeds, callbacks, or complex routing logic that makes the economic outcome harder to summarize completely.

    The boundary condition is especially important for approvals. An approval is not the same as a transfer, but it can give a contract permission to transfer tokens later, subject to the allowance. Revoking unused approvals reduces one attack surface, yet it does not repair a compromised protocol, reverse a completed transaction, or protect a user who signs a new malicious approval. Approval hygiene is risk reduction, not risk elimination.

    There is a related distinction between wallet-level and protocol-level security. A wallet can identify suspicious patterns, flag a risky contract, and make the expected result clearer. It cannot prove that a lending market’s collateral model will remain solvent, that an oracle will remain accurate, or that a bridge’s validators will behave honestly. The wallet helps with authorization risk; it does not fully underwrite economic, governance, liquidity, or smart-contract risk.

    A practical framework for assessing a new dApp

    Before connecting, verify the domain through a trusted route rather than a search advertisement or unsolicited message. Check the intended network and confirm that the dApp’s purpose matches the action being requested. A site that claims to offer a token claim but requests permission to move unrelated assets deserves immediate suspicion.

    Before signing, classify the request. Is it a read-only connection, a message signature, an approval, a swap, a deposit, a withdrawal, or an administrative action? These categories carry different consequences. A message signature may not move funds immediately, but it can still be dangerous when used in phishing systems or off-chain authorization schemes. A token approval may appear routine while creating a future pathway for asset movement.

    Then compare the intended economic result with the simulated result. Look for the assets leaving the wallet, the assets arriving, the spender address, the approval amount, and any unexpected contract calls. If the result is unavailable, contradictory, or too vague to interpret, uncertainty itself is a risk signal. Do not treat a missing simulation as evidence that the transaction is harmless; it may simply mean the action is too complex or unsupported to model confidently.

    Finally, size the position according to the uncertainty that remains. A new protocol with limited history, unaudited code, concentrated liquidity, or upgradeable administration may warrant only an amount the user can afford to lose. This is not pessimism. It is a way to keep a single contract failure from becoming a total custody failure. Separating wallets can also reduce blast radius, although it cannot prevent mistakes if the same seed phrase, browser session, or signing habit links them operationally.

    What to watch as wallet integration evolves

    Recent project messaging dated August 24, 2026, emphasizes Rabby Wallet’s support for Ethereum and EVM chains, along with extension access through browsers such as Chrome and Brave. The meaningful development is less the number of supported networks than the challenge it creates: as users move across chains, the wallet must help them distinguish network context, contract identity, token representation, and transaction consequences. Multichain convenience can reduce friction, but it can also increase the chance of sending assets on the wrong network or trusting a familiar-looking dApp in an unfamiliar environment.

    A plausible next phase of wallet design is more useful transaction explanation, not simply more warnings. The strongest systems would help users compare intended action with predicted state change, identify unusual permissions, and make uncertainty visible. That remains conditional on reliable simulation infrastructure and clear protocol metadata. If those inputs are incomplete, a polished warning system could create false confidence—the dangerous belief that everything not flagged has been verified.

    The durable lesson is simple but easy to overlook: the wallet is part of the security boundary, not the whole boundary. Use simulation as a decision aid, approvals as permissions to review, and dApp integration as an ongoing trust relationship rather than a one-click event. The safest DeFi workflow is not the one with the fewest prompts. It is the one in which every important prompt can be understood before a key is used.

    Frequently asked questions

    Does transaction simulation make a DeFi transaction safe?

    No. It can reveal likely balance changes, approvals, and failures before signing, which improves decision quality. But it is based on assumptions about current blockchain state and contract behavior. It cannot guarantee future execution, protocol solvency, honest governance, or protection from every phishing and key-compromise scenario.

    Should I use one wallet for all DeFi activity?

    Using one wallet is convenient but increases concentration risk. A more resilient setup separates long-term holdings from experimental or frequent activity, potentially adding a hardware signer for higher-value assets. The right arrangement depends on the amount at risk, the user’s operational discipline, and how much complexity they can manage without introducing new mistakes.

    What is the most important detail to check before approving a dApp transaction?

    Check the expected state change: what leaves the wallet, what arrives, which contract receives permission, and whether the approval amount is appropriate. If those details do not match the action you intended, stop. A familiar interface or popular protocol name is not a substitute for verifying the actual transaction.